Original source: spectrum.ieee.org — 28 Zero-Day Findings in Under Two Days. Is Robotics Security Keeping Pace?
A Tokyo-based cybersecurity company has identified 28 previously unknown vulnerabilities in robotics software and tools in less than two days. According to spectrum.ieee.org, VicOne used AI-assisted research to uncover these zero-day weaknesses, raising urgent questions about how quickly the robotics field can respond to new security threats.
What happened
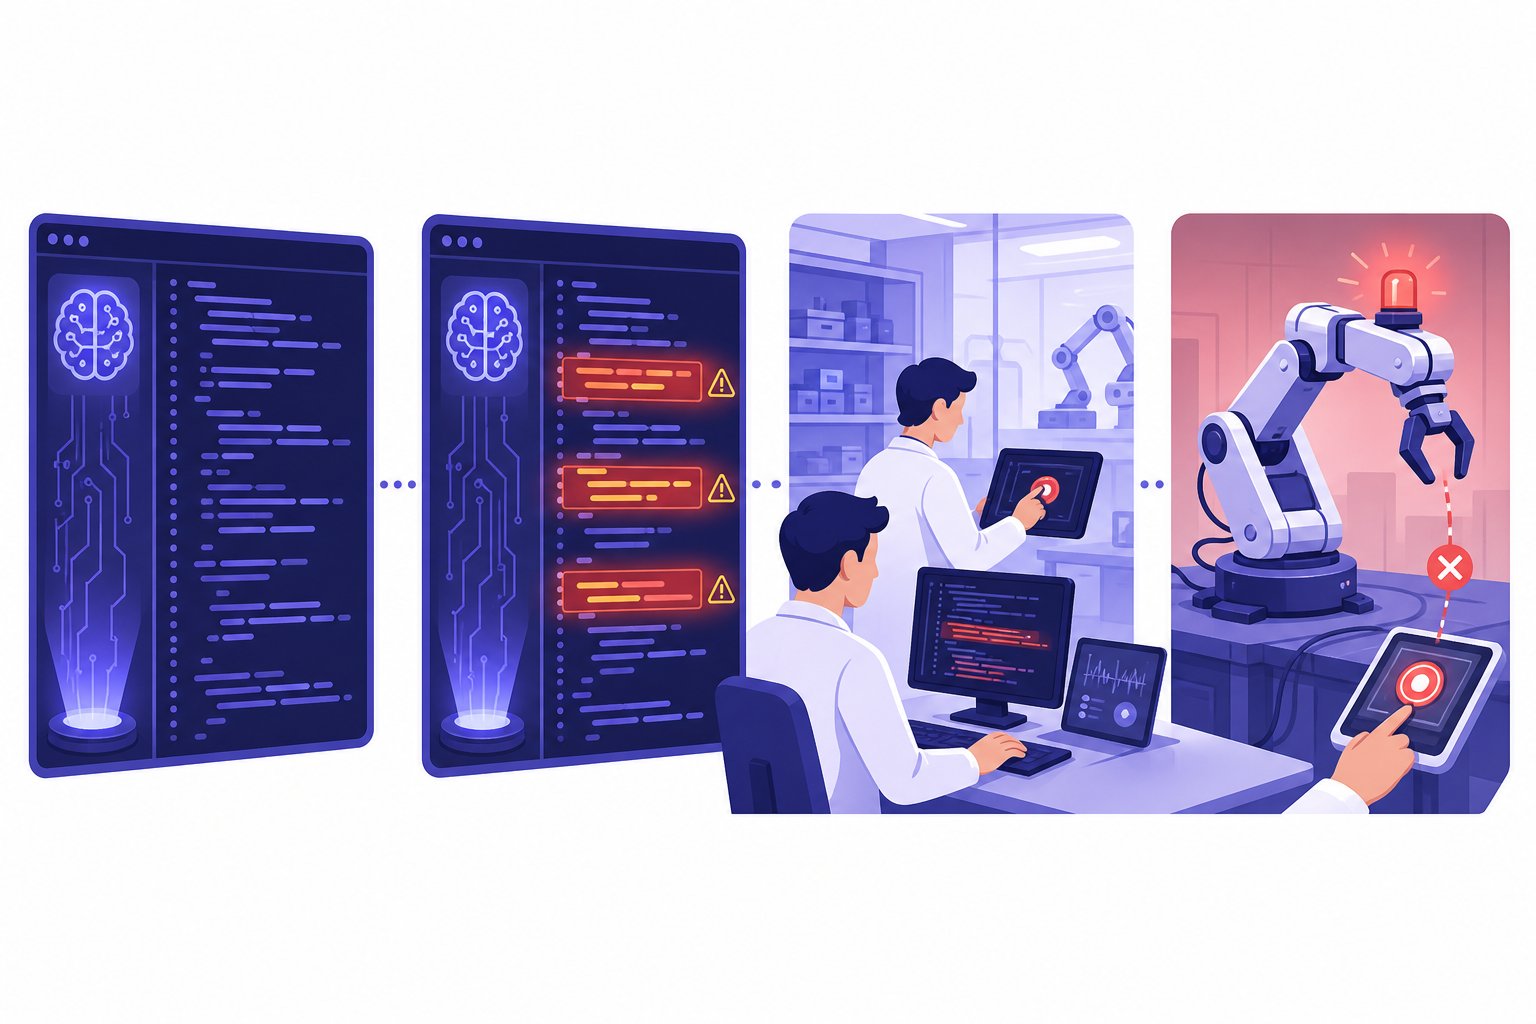
VicOne, a company specializing in cybersecurity for vehicles and robots, used artificial intelligence to analyze software and tools in the Physical AI ecosystem. In under two days, the team found an initial set of 28 zero-day vulnerabilities. These vulnerabilities affected projects developed or maintained by major technology companies, including Google, NVIDIA, and Meta, according to spectrum.ieee.org.
All 28 findings are classified as zero-day vulnerabilities, meaning they were previously unknown and had no fixes available at the time of discovery. The final count may change after further review by vendors and relevant authorities. Some of the findings do not yet have official CVE tracking numbers.
The affected tools are used throughout the robotics lifecycle: development and training, simulation and validation, and deployment and runtime. According to VicOne, 75% of the findings involved systems for development, training, simulation, or validation. This highlights the risk that vulnerabilities can be introduced before a robot is even deployed.
VicOne demonstrated the seriousness of these weaknesses in a separate test, where researchers exploited a vulnerability that prevented a robot’s remote-stop command from working. This example shows how a compromised software component could undermine critical safety features.
The company notes that AI can speed up the process of finding weaknesses, but robotics teams still need to validate fixes and ensure they do not create new problems. Teams may need to use temporary measures, such as restricting access, while permanent fixes are developed and tested.
Why it matters for researchers
The rapid identification of 28 zero-day vulnerabilities using AI signals a new era for cybersecurity in robotics. Researchers, developers, and engineers in the field must be prepared for faster cycles of vulnerability discovery, both from defenders and potential attackers. This means that the time available to respond to newly found vulnerabilities is shrinking.
For those working on robotics software, simulation tools, or AI models, the findings highlight the importance of integrating cybersecurity into every stage of development and deployment. The potential for vulnerabilities to affect robot training, testing, and real-world control increases the demand for security expertise in robotics teams. Startups and established companies alike may need to invest more in security reviews, automated analysis, and post-deployment monitoring.
The industry is likely to see increased demand for cybersecurity specialists who understand both robotics and software vulnerabilities. As AI accelerates both discovery and exploitation of weaknesses, funding and research may shift toward tools and processes that can keep pace with these developments.
Where to dig deeper
- Read the original report at spectrum.ieee.org
- Track new papers on cybersecurity with Seamless
- Explore VicOne’s approach to Physical AI cybersecurity and their white paper on robot safety and cybersecurity.
This article summarises public reporting. Facts as reported by spectrum.ieee.org; read the original for full details.